
Recent frequent asset loss incidents in the decentralized finance (DeFi) sector due to improper management of authorization scopes in contract interactions stem primarily from users’ failure to scrutinize unlimited authorization mechanisms, allowing malicious contracts to freely transfer wallet assets. The industry is currently promoting segmented account operations and periodic authorization revocation to reduce asset exposure, while security audit standards are tightening accordingly.
The background to such incidents lies in the decentralized ecosystem’s overreliance on authorization mechanisms. To enhance user experience, mainstream protocols default to large or unlimited authorizations without offering fine-grained limit options. While this design improved capital efficiency in its early days, unlimited authorization has become the primary vector for on-chain asset drainage as attack techniques evolve, necessitating urgent technical convergence.
Security Incidents Caused by Excessive Authorization Scopes
Recent multiple decentralized application (dApp) security incidents have exposed the issue of uncontrolled authorization scopes in contract interactions. When participating in liquidity mining or claiming airdrops, users are often required to grant unlimited authorization, enabling contracts to transfer all user tokens of the same type without requiring a second signature. If the contract contains vulnerabilities or is maliciously exploited, assets can be drained instantly and are extremely difficult to recover.
Why Does Unlimited Authorization in Contract Interactions Lead to Asset Theft?
Unlimited authorization essentially transfers full control of assets to the smart contract. Once the user signs the authorization transaction, the contract gains permission to make arbitrary transfers within the specified token balance. If the contract code contains backdoors or is compromised, hackers can directly invoke the transfer function to move tokens out without requiring further user confirmation. Another risk lies in the persistence of authorization: even after ceasing to use an application, the authorization remains valid indefinitely, allowing attackers to lie in wait and strike when conditions are favorable.
Industry Prevention Measures and Key Focus Areas
In response to risks posed by overly broad authorization scopes, security firms and decentralized protocols have begun adjusting their risk control strategies. Some platforms have introduced temporary or per-transaction authorization mechanisms to limit the number of tokens a contract can manipulate. Additionally, the community recommends using dedicated authorization management tools to regularly query and revoke suspicious contract authorizations, thereby reducing asset exposure and enhancing overall fund safety.
The market should closely monitor the progress of on-chain risk control tool upgrades, as well as regulatory requirements regarding the compliance of authorization mechanisms in decentralized protocols. Before interacting with new projects, investors should verify whether the contract has undergone a security audit and use isolated addresses to separate interaction assets, preventing main wallets from being compromised due to excessive authorization and thereby controlling risk exposure at the source.

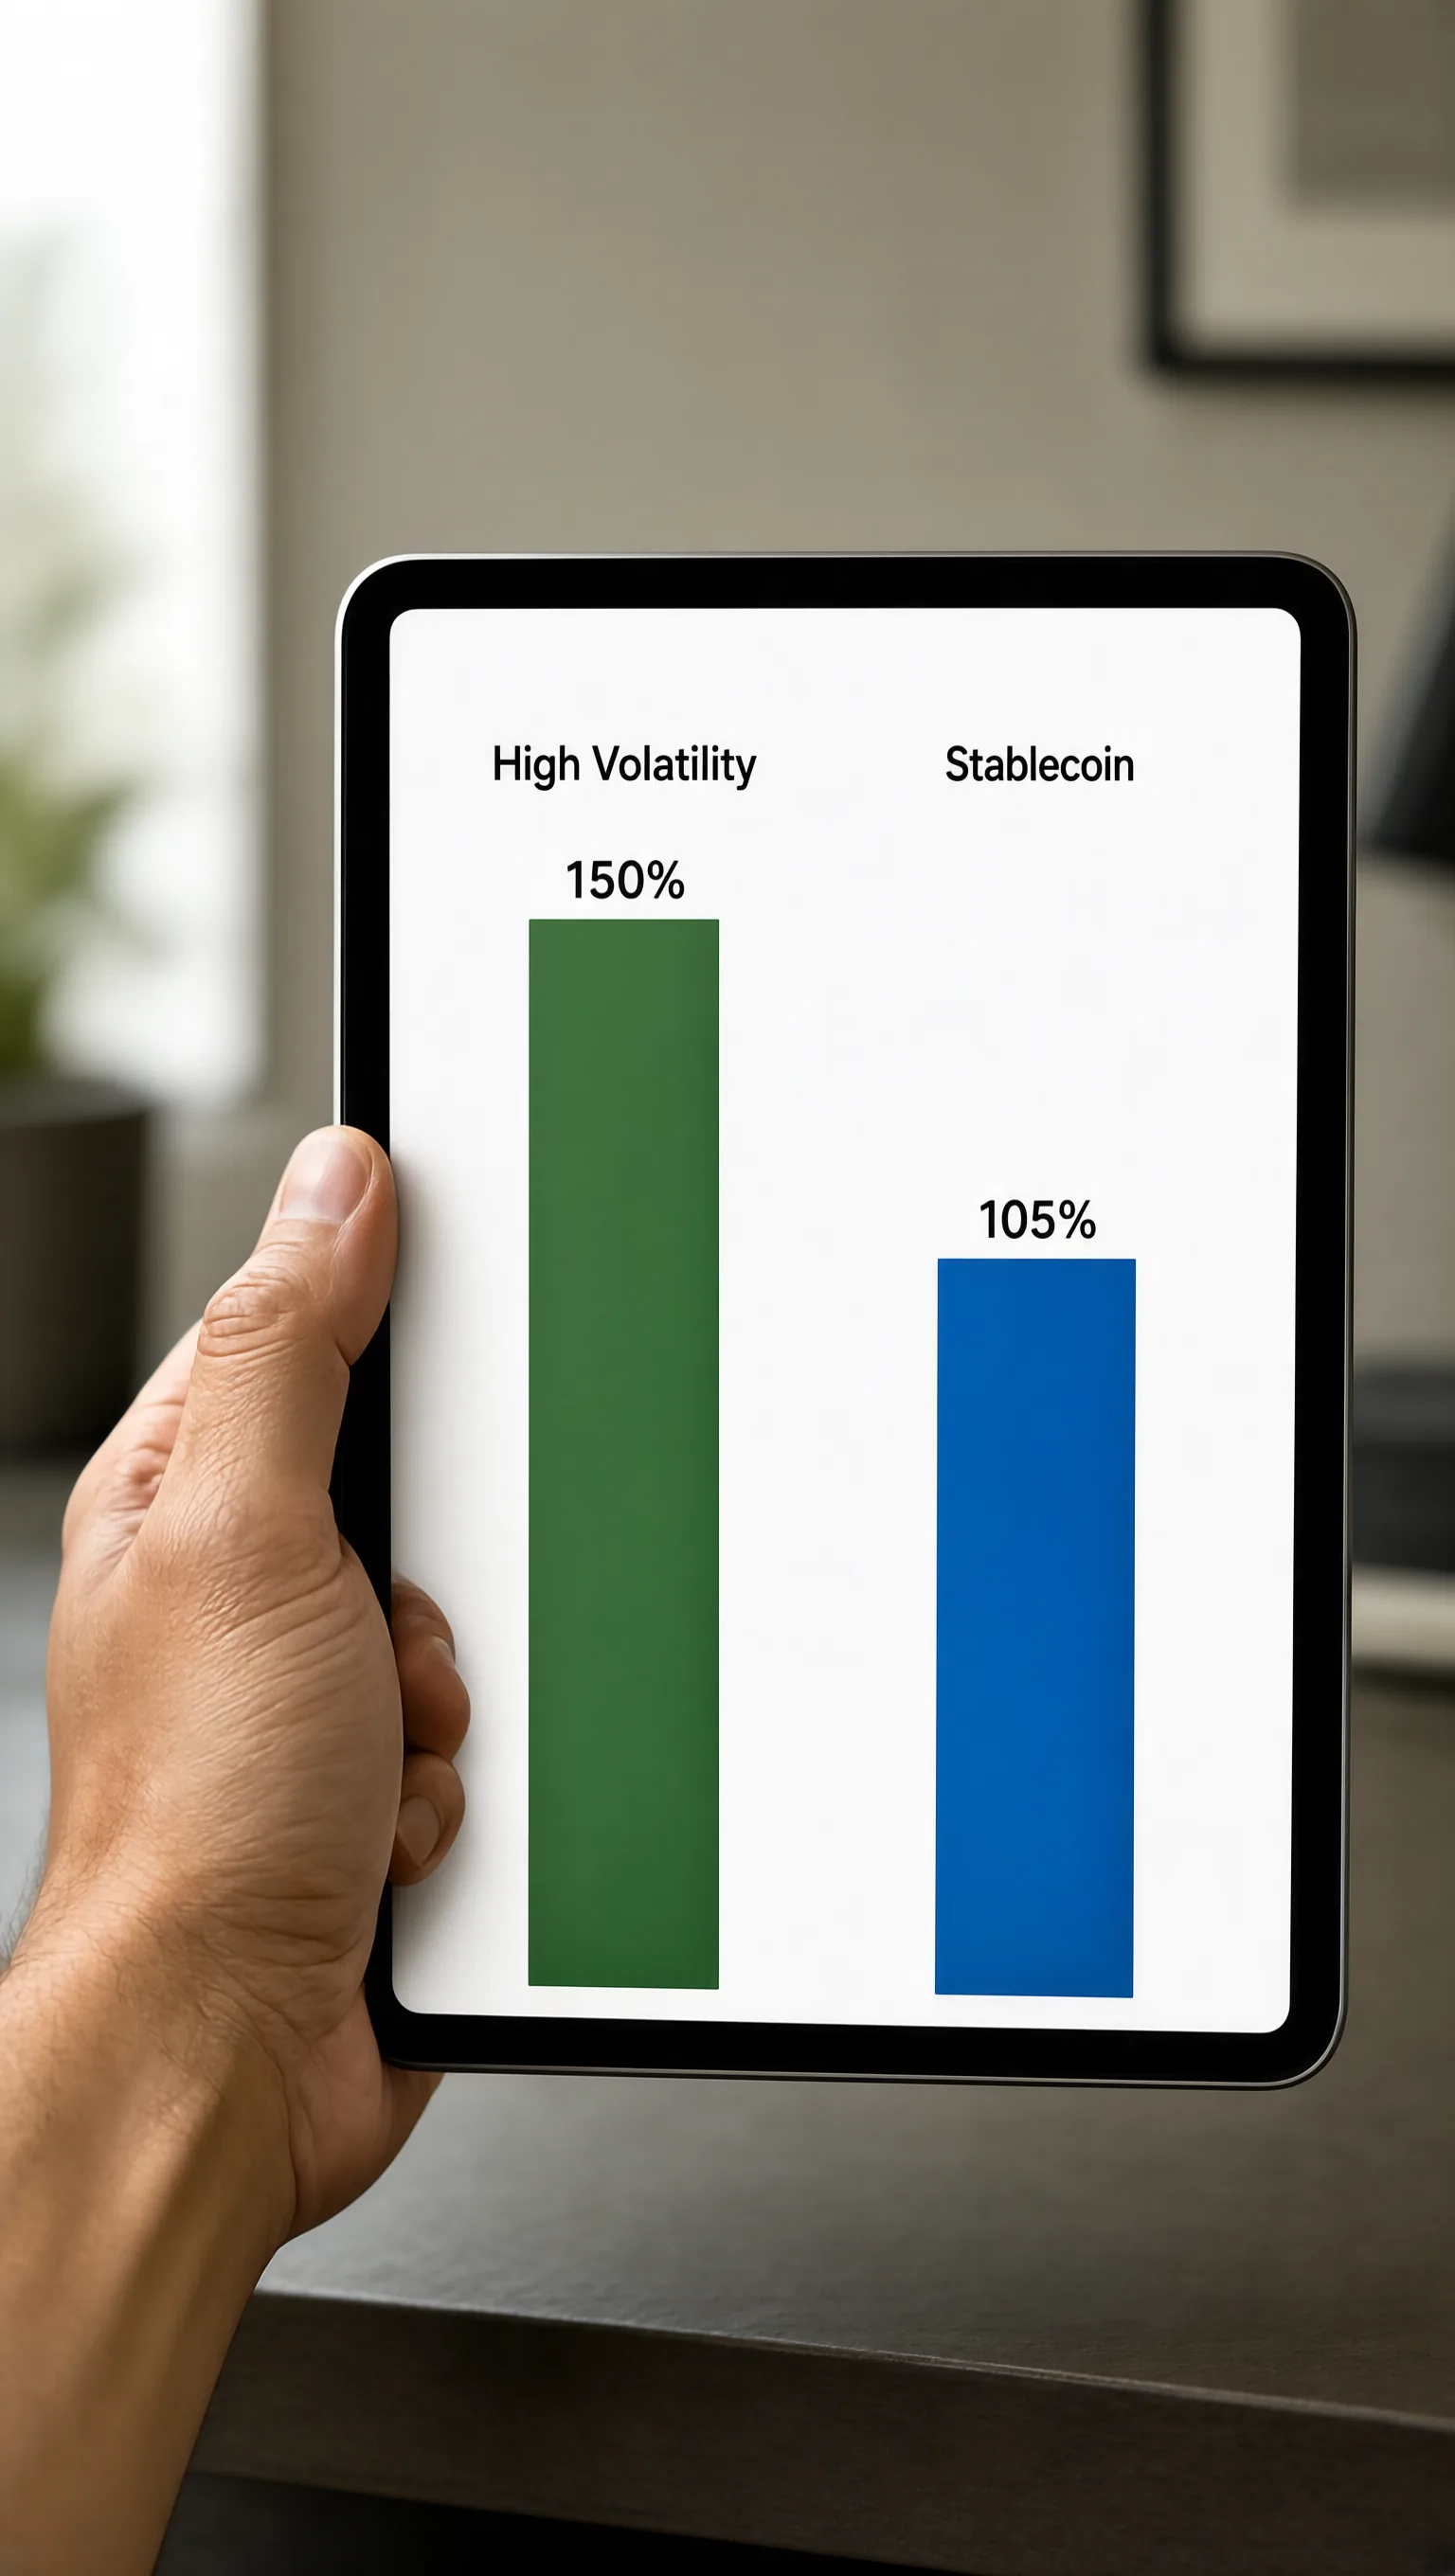
Bitcoin has moved sharply lately, so the upside and the risk need to be measured together.
Checking network fees and platform rules before a transfer is especially important for beginners.
The article explains wallet security, exchange selection, and risk control in a practical way.